Threat Intelligence Management
Aggregates, normalizes, and contextualizes threat data from open-source feeds, premium feeds, and internal telemetry. Sources include reputable news outlets, social media, the dark web, and more.

Infected Industries integrates with the security products already in your environment. Intel feeds and confirmed malicious indicators are delivered to your block lists, and alerts are enriched where your analysts work. Automated lookups return that context in place, so your SOC spends less time on research and responds with greater productivity, accuracy, and speed.
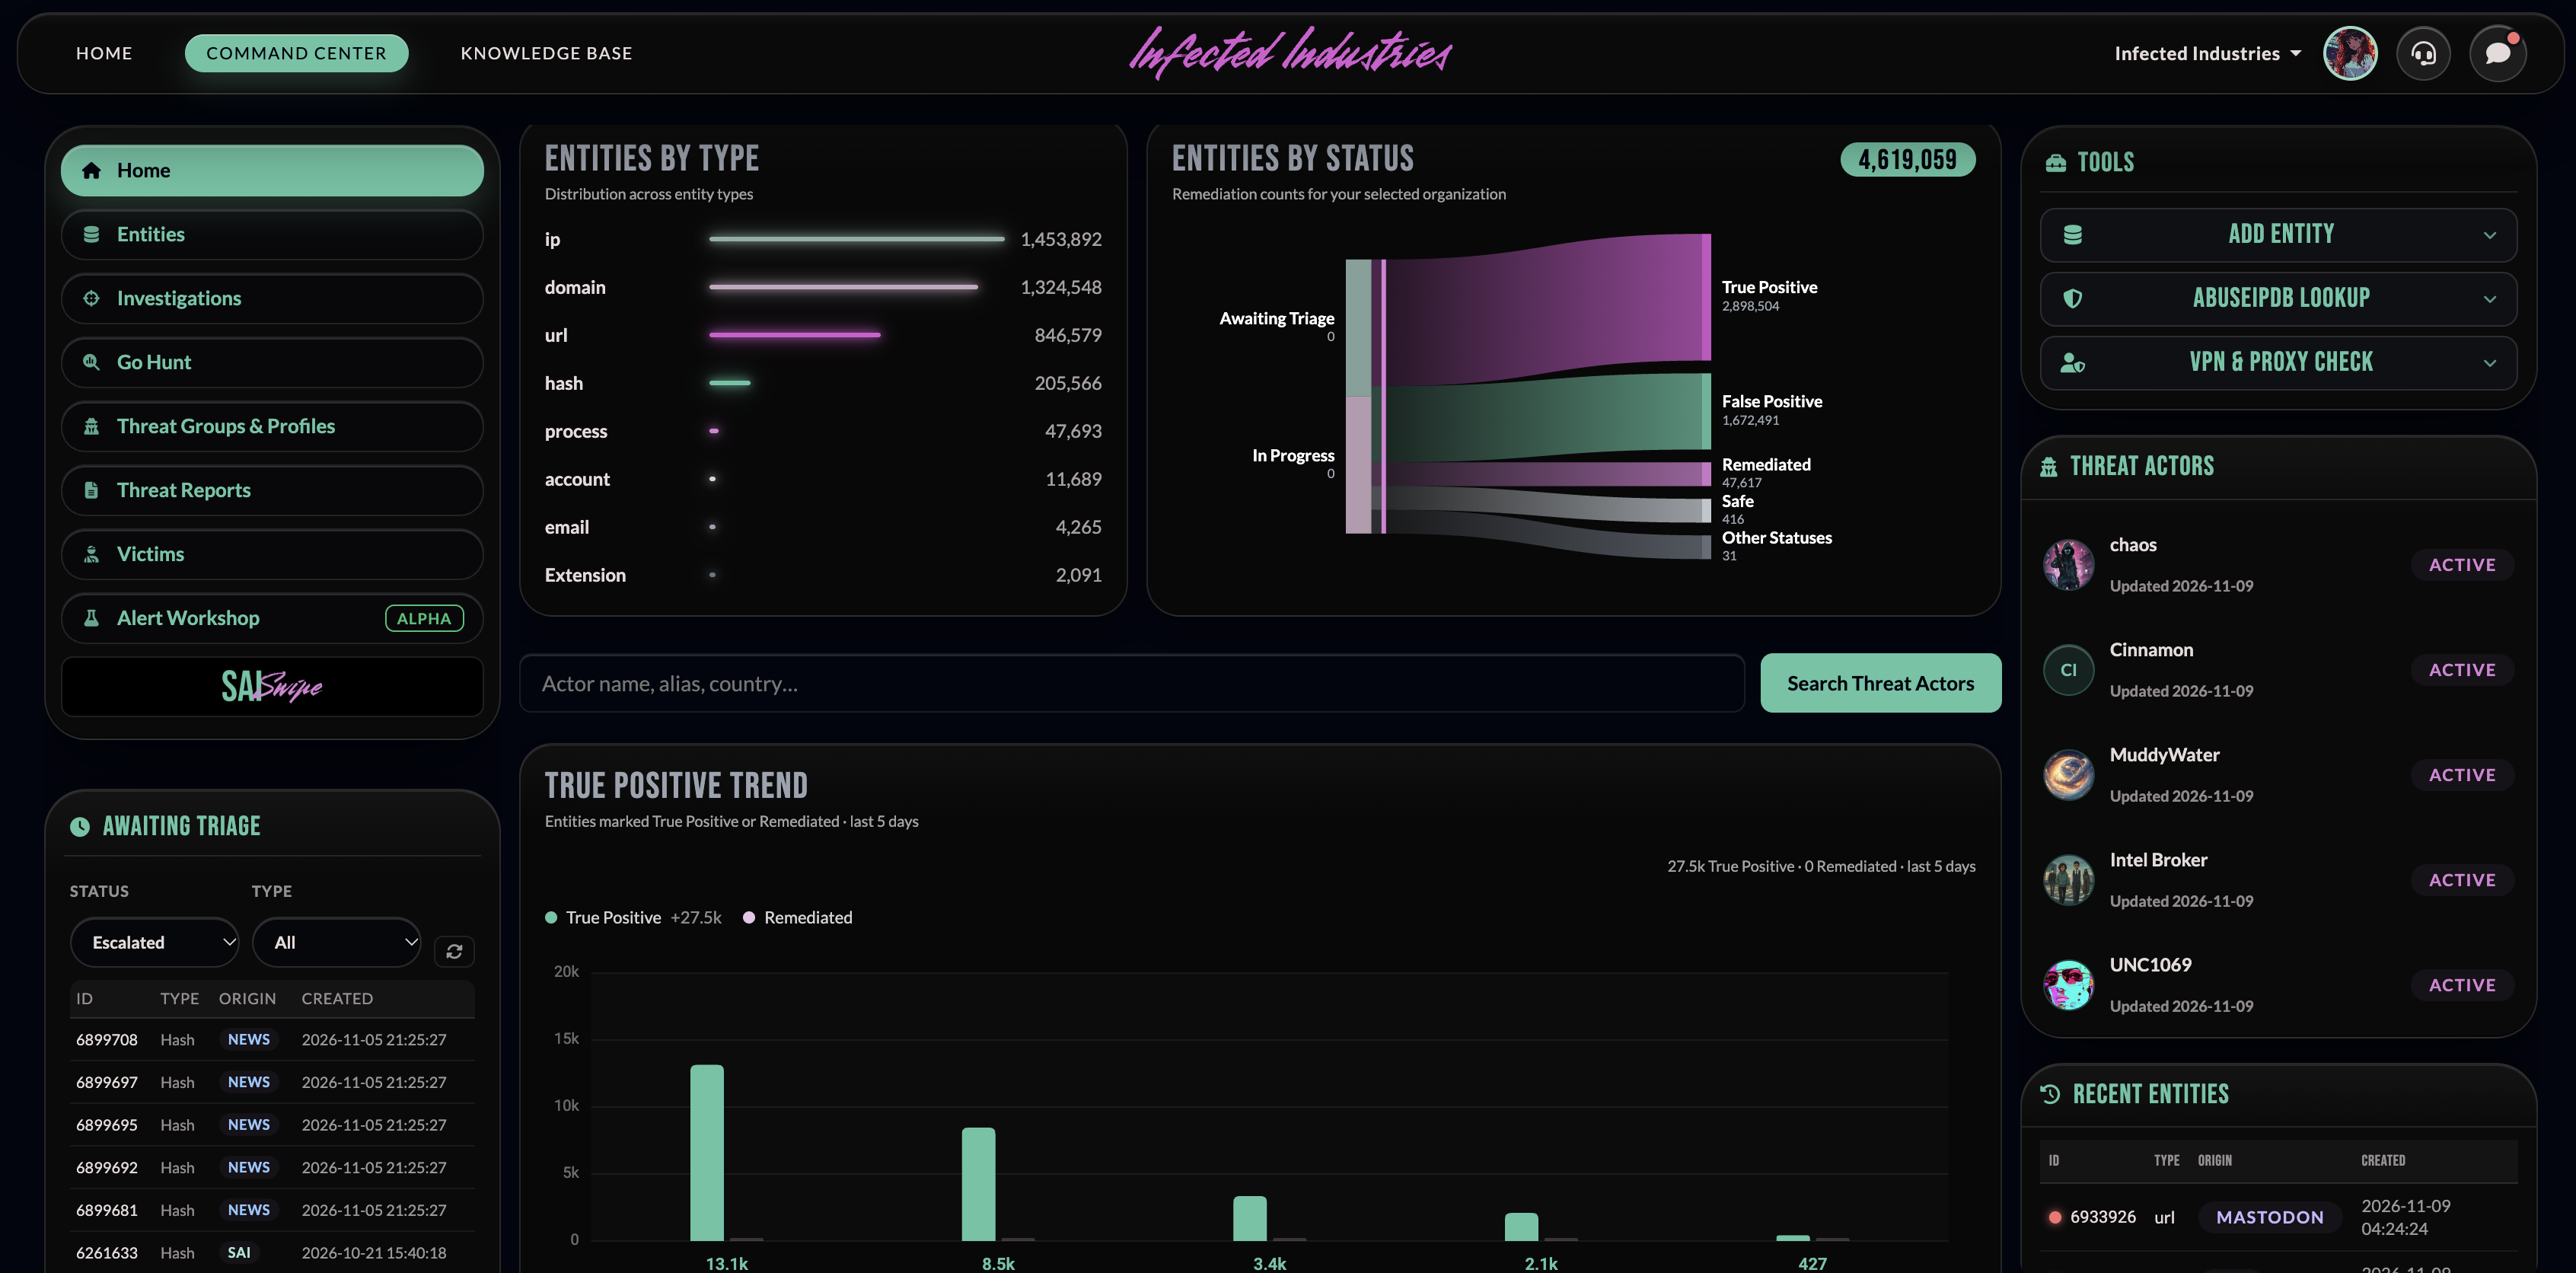
Aggregates, normalizes, and contextualizes threat data from open-source feeds, premium feeds, and internal telemetry. Sources include reputable news outlets, social media, the dark web, and more.
Automated workflows streamline incident response, push indicators to security controls, and speed up SOC mitigations. Optional autoremediation can act on true positive IOC feeds in platforms such as Microsoft Sentinel and CrowdStrike NextGen SIEM.
Security teams analyze, track, and share threat intelligence safely inside structured workflows or anonymized communities.
Connect Infected Industries to your existing AI SOC or ticketing platform. Incoming alerts arrive with true positive IOC lookup, IP address lookup, threat actor attack path matching, and more. The lookups run for you. The answers land in your environment.
Analysts spend less time opening research tools and more time deciding. Automation runs the lookups and displays the result next to the alert.
Known malicious context, threat actor paths, and finished intel sit on the alert itself, so fewer details get missed in the handoff between consoles.
Intel feeds and confirmed IOCs can go straight to block lists, and custom detections can be pushed to multiple EDR products without rebuilding the workflow.
SAI is the AI agent within the Infected Industries platform, providing direct messaging, triage, and access to operational tools.
The same capabilities are available on mobile through SaiSwipe. SAI is powered by SAIdream, a custom LLM framework developed by analysts for analyst workflows. SAIdream brings intelligence, automation, and action into a single experience.

Cyber threat intelligence protects an organization only when it reaches the controls and the analysts who act on it. Infected Industries gathers reporting from reputable news outlets, social media, the dark web, and other sources, then turns it into threat reports, threat actor profiles, YARA rules, and Sigma rules. Custom detections can be pushed to multiple EDR products. The faster that intelligence lands in the products you already run, the sooner those products can help contain a cyber incident.
The same reporting trains the team in current practice. Analysts stay informed about ransomware activity, cyber breaches, and the threat intelligence behind them without leaving their existing tools. That context shows what to watch, which indicators matter, and how mature teams respond. An informed security team makes faster, more consistent decisions, and the function as a whole is elevated.
Autoremediation remains optional. Enable it for true positive IOC feeds that connect to platforms you already run, including Microsoft Sentinel and CrowdStrike NextGen SIEM.
Analysts access SAIdream through private messaging in Infected Industries, and on Android through SaiSwipe. SAIdream is an operational interface, not only a chat window. From that interface, SAI can run platform tools, create alerts, and deploy configurations directly to your environment throughout the workday.
The Incident Response Plan Preparation module helps response teams understand their plans, workflows, and the steps to follow when a plan is activated.
Want to learn more about threat actors and their attack paths? Need to create detection rules or deploy them to your environment? Just ask. SAIdream brings security insights and action together through natural conversation.
SAIdream adapts to your communication preferences, learning style, and sense of urgency, so the experience gets more personal over time. Academic studies and scientific research inform how he responds. He is still nerdy, witty, and snappy. SAIdream is one of the features of Infected Industries.
Analysts should be able to understand an alert without leaving the security tools they already operate. Infected Industries supplies that context directly in the workflow, so the existing team can respond with greater confidence.
Automation runs the lookup tools and displays the results in your environment. Analysts spend less time gathering context and more time acting on it. Productivity, accuracy, and speed improve together.
Intel feeds and known malicious IOCs can go to block lists. YARA rules, Sigma rules, and other custom detections can be pushed to multiple EDR products. True positive IOC feeds can optionally autoremediate in platforms such as Microsoft Sentinel and CrowdStrike NextGen SIEM.
Reputable news outlets, social media, the dark web, open-source feeds, premium feeds, and internal telemetry. We aggregate, normalize, and contextualize that data, and we publish threat reports and threat actor profiles.
No. Infected Industries connects into the stack you already run, including your AI SOC and ticketing platform, and enriches what those tools already show your team.